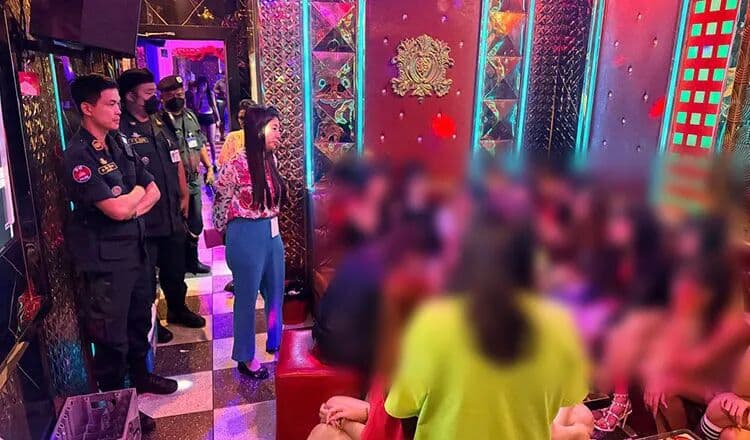
During the raid, officers caught operators actively using laptops and smartphones to communicate with overseas targets via VoIP and messaging apps, unable to produce any valid business licenses. Initial findings indicate that the gang posed as staff from major firms like Amazon and Google, utilizing forged identification documents to phish banking, credit, and ATM card details from victims in the United States, Canada, and elsewhere. In addition, they ran a narcotics parcel scheme, falsely warning targets that illegal drugs were discovered in their packages and coercing payments under the threat of criminal prosecution.
The operation relies on high-pressure scare tactics remarkably similar to those commonly deployed in Southeast Asian fraud compounds. Authorities seized mobile phones, laptops, cash, and vehicles valued at approximately Rs 36.41 lakh. All 20 suspects have been booked under provisions of the Indian Penal Code, the Information Technology Act, and the Indian Telegraph Act, while investigators work to map out the network's internal hierarchy, financial trails, and possible links to syndicates operating both inside and outside India.
ToNanyang Prediction Market: https://tonanyang.cc/webapp/