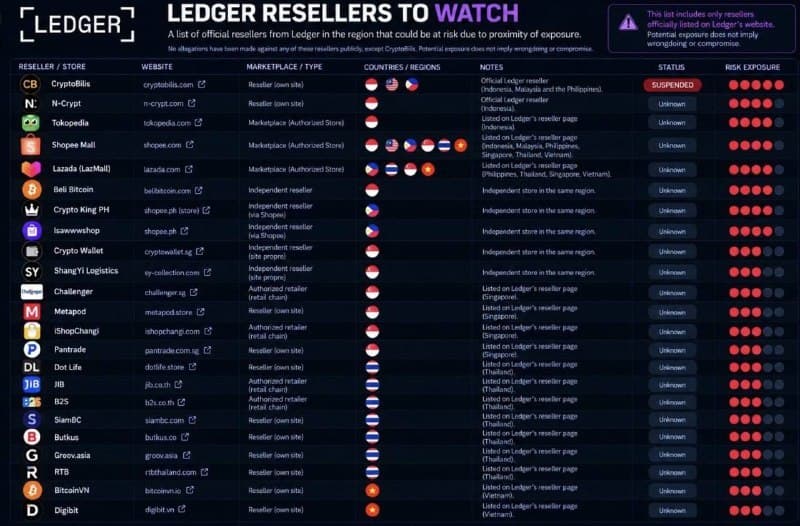
Crypto security analysts recently compiled a watchlist of over 20 third-party distributors facing potential tampering risks. Even big-box chains such as MediaMarkt are not considered safe channels, and tampered devices have already surfaced in the EU. When physical supply chains are breached, the attack vector bypasses standard software safeguards before the box is even opened.
For cross-border operators and overseas holders who rely on cold storage for asset security, this is a direct hazard. Any hardware wallet acquired through third-party channels within the past 90 days should not be initialized if untouched. If funds have already been deposited, the safest route is to order a fresh unit directly from the official website and transfer everything using a newly generated recovery phrase.
Keep one core rule in mind: recovery phrases must be generated and displayed exclusively on the hardware screen itself. Any pre-printed or pre-filled seed card found inside the box is undeniable proof of a malicious swap. For substantial treasury holdings, transitioning to multi-signature setups with independent devices or MPC solutions is worth serious consideration.
Like for points, predict to win points|ToNanyang Prediction Market: https://tonanyang.cc/webapp/