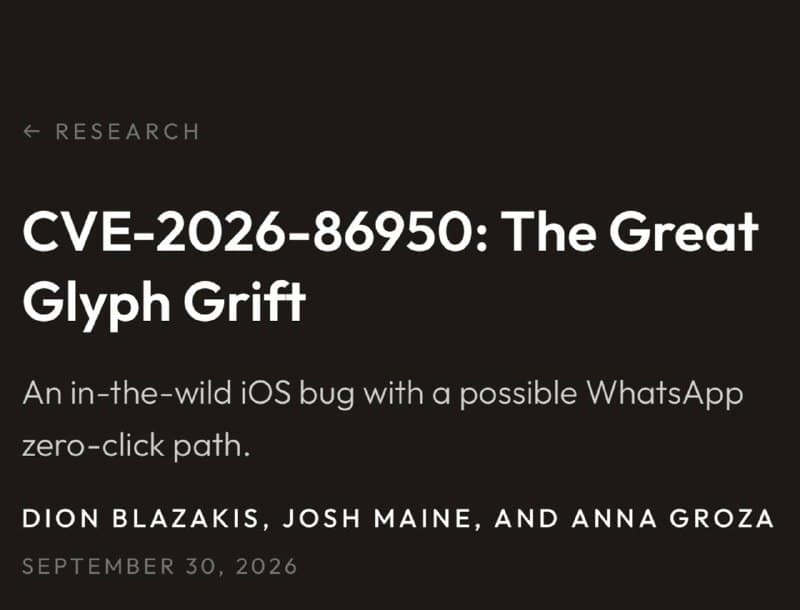
Cybersecurity firm Calif has disclosed a high-severity in-the-wild flaw affecting Apple systems (CVE-2026-86950). Attackers can embed specially crafted fonts into a malicious PDF and send it over WhatsApp. Simply receiving the document triggers the exploit in the background as the system renders a thumbnail, requiring zero user interaction.
The root cause lies in Apple's CoreGraphics engine, where oversized coordinates cause an integer wrap issue, prompting an out-of-bounds write due to an underestimated memory buffer. The vulnerability has already been leveraged in precision targeted attacks. Apple and Meta have both pushed out patches, and users are strongly urged to update their devices immediately.
ToNanyang Heat Week|check in & spin for Premium