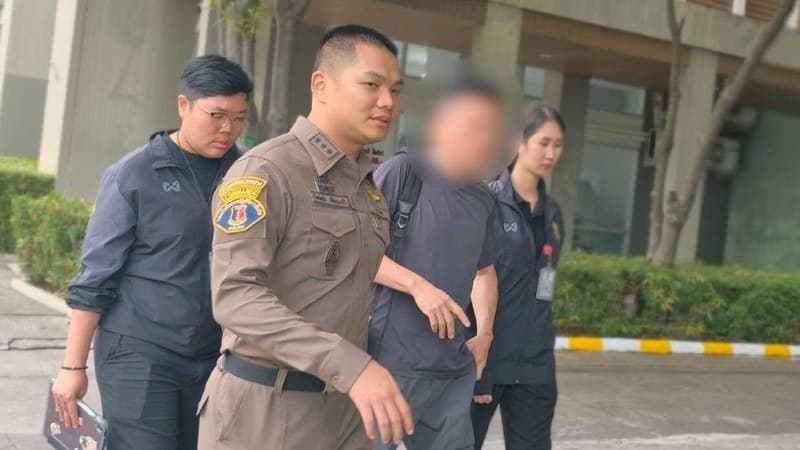
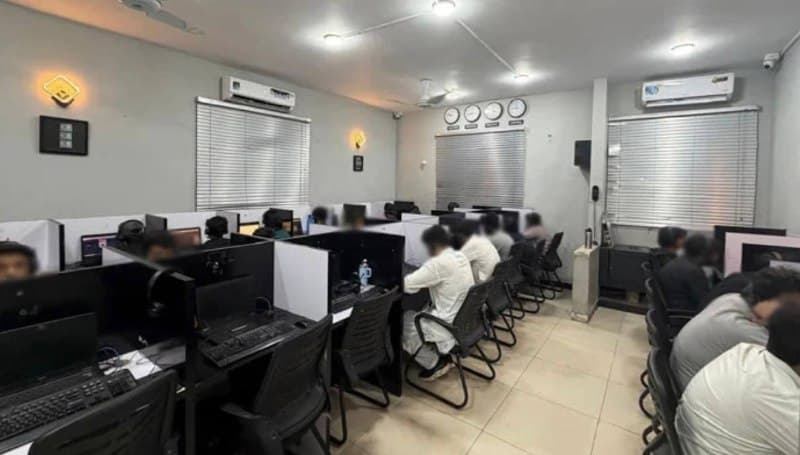
Investigators stated that staff posed as representatives of legitimate US financial institutions to harvest Social Security numbers, phone numbers, dates of birth, and debit or credit card details. The collected records were logged into an internal CRM system and forwarded upstream to execute unauthorized transactions.
Seized CRM software, computer hardware, and client databases are now undergoing digital forensic analysis as police continue tracing the money trail and identifying the wider network.